
TECHNOLOGY //
Operating systems
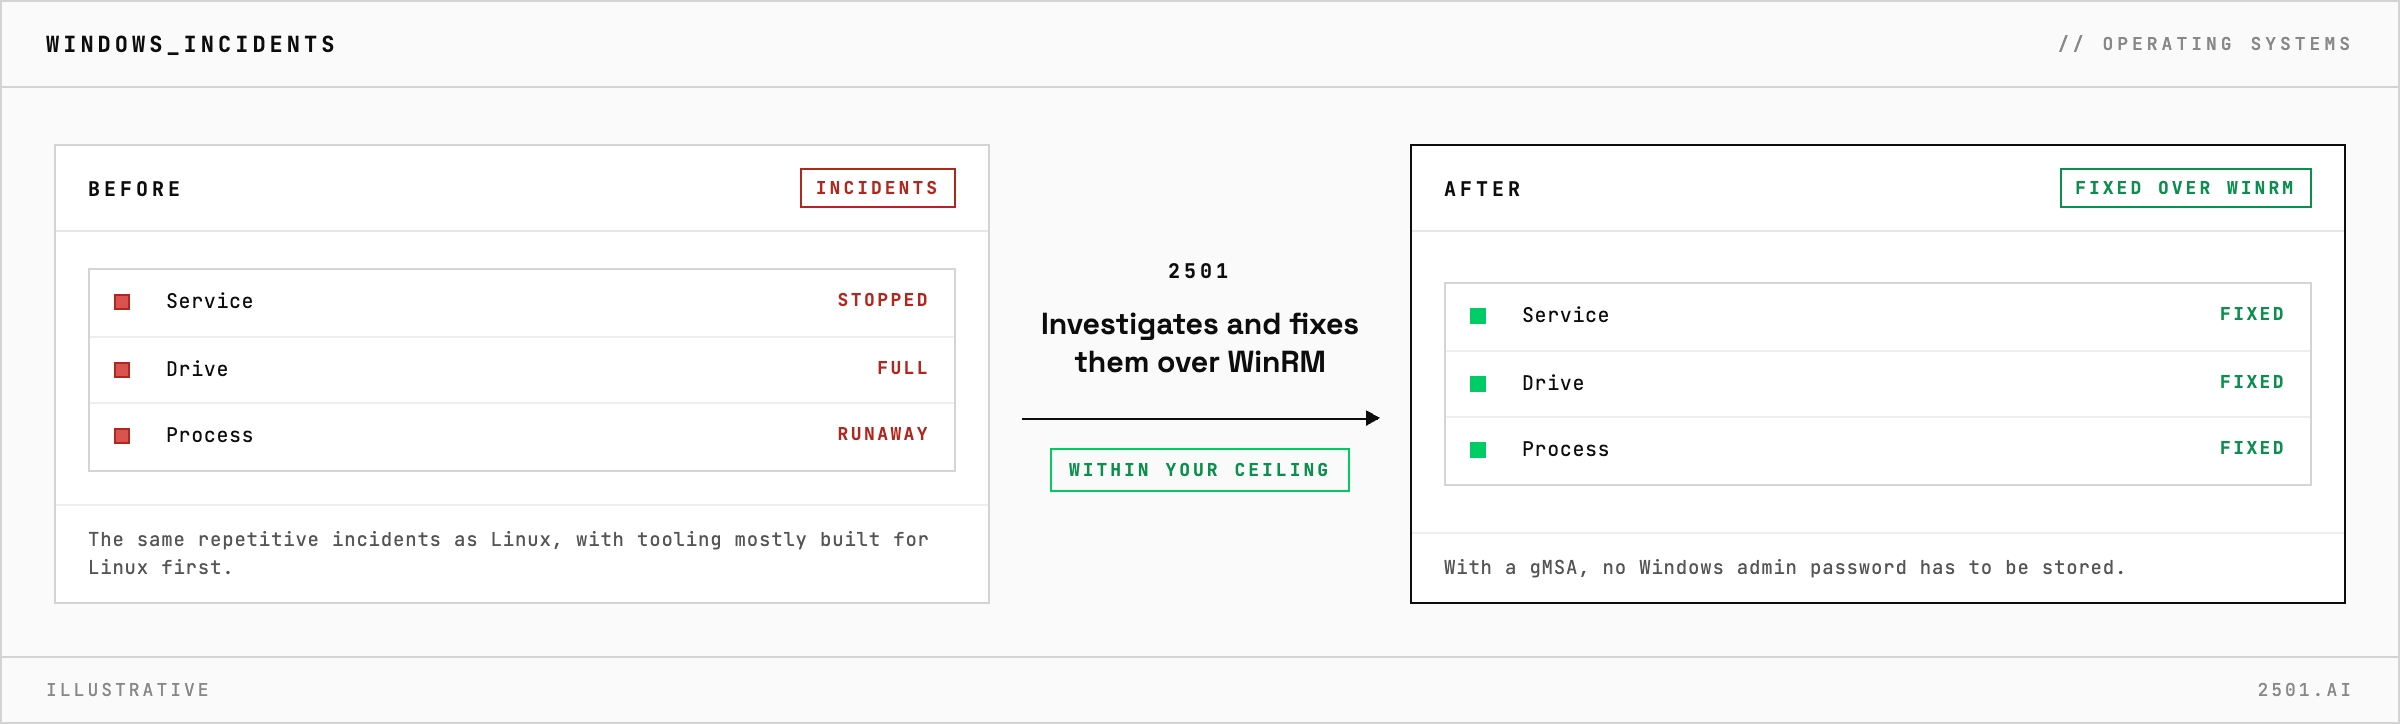
2501 investigates and fixes Windows Server incidents over WinRM and PowerShell, and can sign in with a gMSA so no Windows admin password is stored.
TICKETS FROM
ServiceNow or another ITSM
CATEGORY
Operating systems
AUTONOMY
Investigate only, with a person, or on its own
DEPLOYMENT
On-prem, cloud or hybrid
█
TECHNOLOGY_BRIEFING
// WHAT 2501 DOES
2501 works on Windows Server the same way it works on Linux: it connects over WinRM, runs PowerShell remotely, and investigates and fixes incidents on the host. It can sign in with a group Managed Service Account (gMSA), so no long-lived Windows admin password has to be stored.
Windows estates carry the same repetitive incident load as Linux ones (a stopped service, a full drive, a runaway process), but the tooling for automating it has mostly been built for Linux first.
Windows specialties take these requests from your ticketing system. Disk Manager Windows handles drive capacity alerts with investigation, safe cleanup and volume reporting, Services Manager Windows manages services on Windows hosts, including containerised workloads, and SysOps Windows carries out general Windows Server operations over PowerShell. For Active Directory, the Active Directory Operator covers user and group lifecycle, group policy investigation, replication and domain controller health. With a gMSA, Active Directory manages the password and 2501 reads it only when it connects, and one setup can serve every host that shares the account. What the agent changed, and why, is always reported.
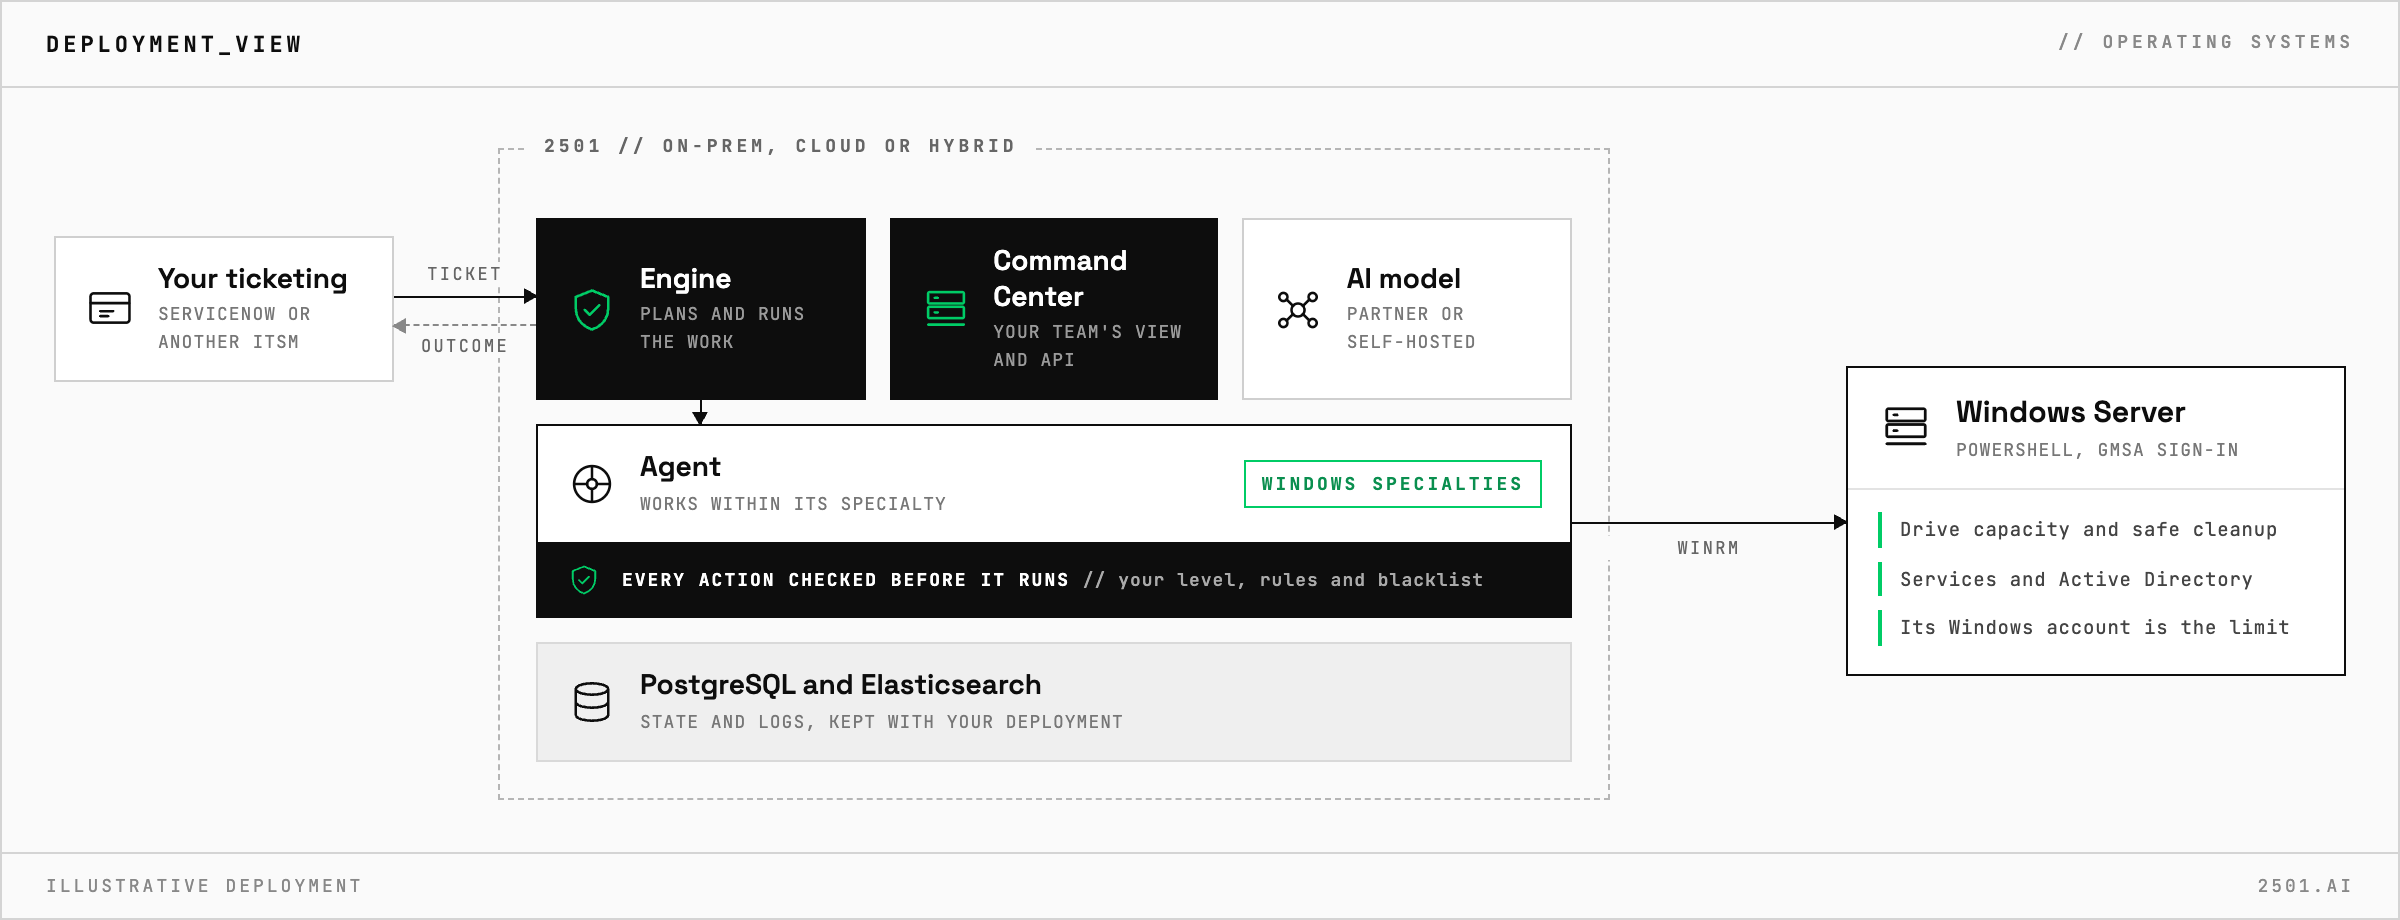
How does 2501 connect to a Windows server? Over WinRM, the Windows Remote Management protocol behind PowerShell remoting.
Can it work without storing a Windows admin password? Yes, with a gMSA. Active Directory manages the password, and 2501 keeps only the credential of the directory account it reads it with.
Is the connection encrypted without HTTPS? Yes. Sessions are encrypted even over plain HTTP, and HTTPS is supported too.
> READY_TO_DEPLOY
Book a technical demo and walk through your own environment with the 2501 team.
