AGENT SPECIALTY //
Observability and security
2501's Certalert Investigator checks whether a vulnerability alert is really exploitable on your RHEL-based hosts, reclassifies its severity with evidence and changes nothing.

TICKETS FROM
ServiceNow or another ITSM
CATEGORY
Observability and security
AUTONOMY
Investigate only, with a person, or on its own
DEPLOYMENT
On-prem, cloud or hybrid
█
SPECIALTY_BRIEFING
// WHAT 2501 DOES
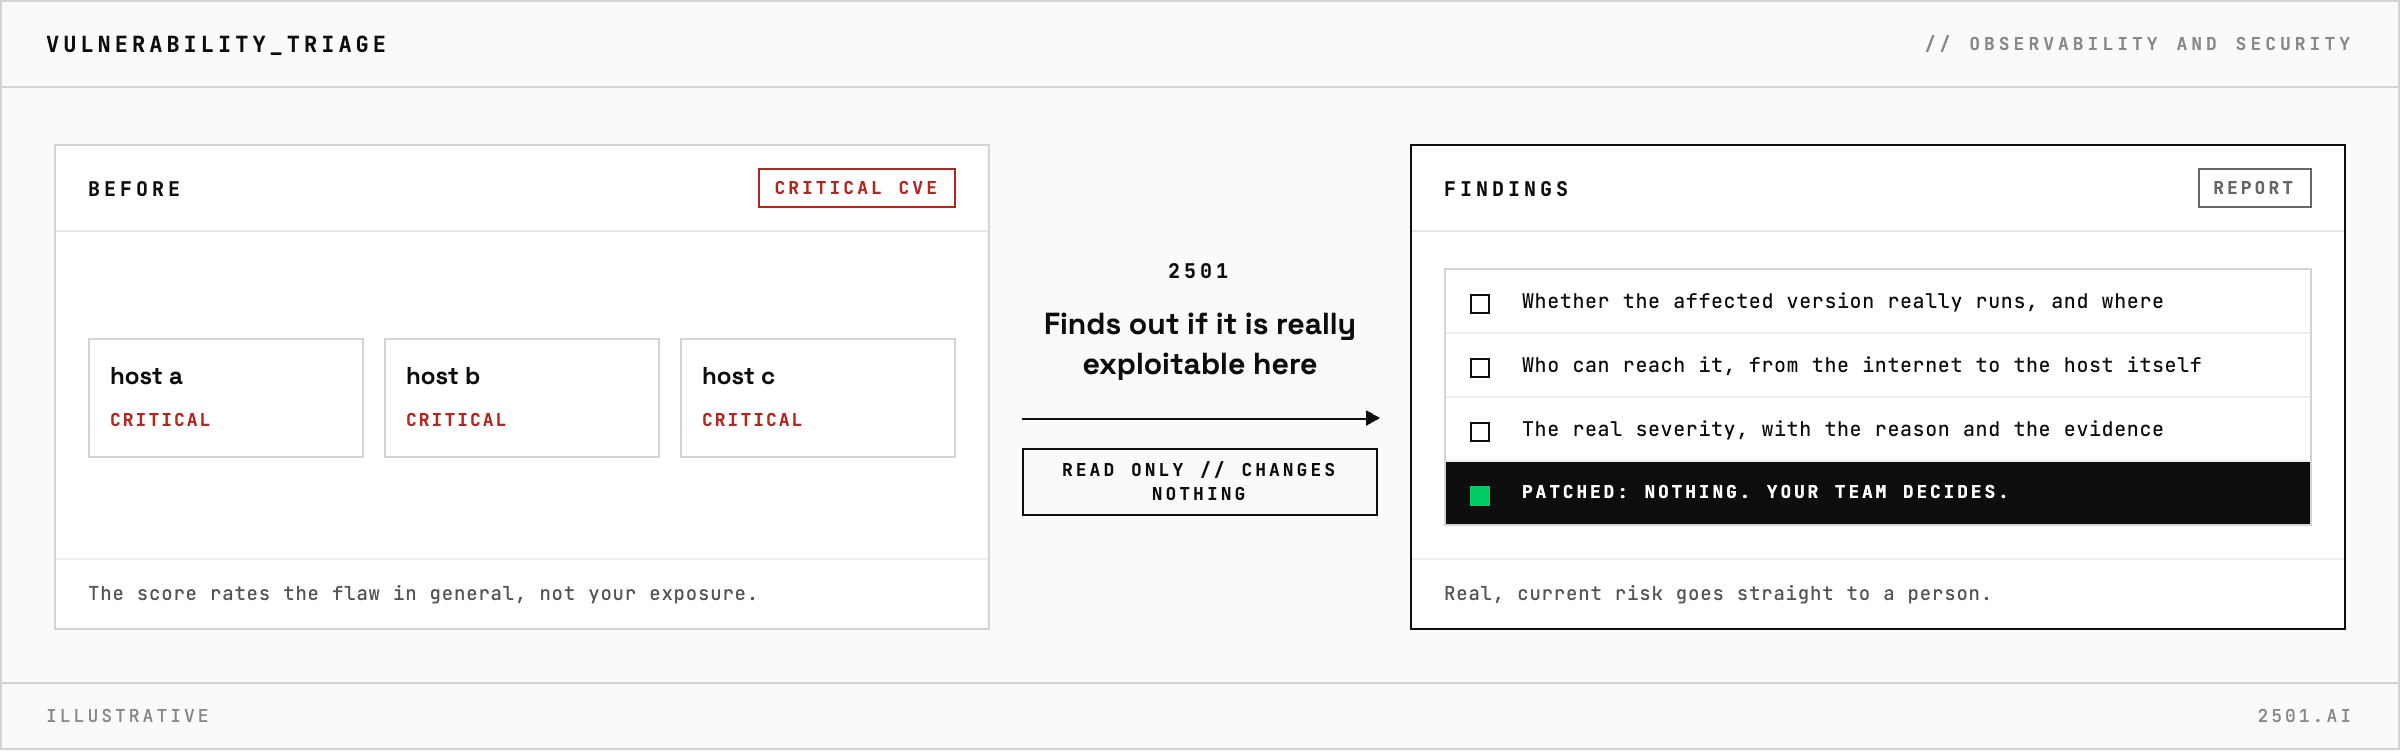
Certalert Investigator is 2501's read-only specialty for vulnerability alerts on RHEL-based systems: it works out whether a flagged vulnerability can really be exploited where it runs, and reclassifies the alert's severity with evidence. It never patches, restarts or changes anything.
A scanner flags a critical vulnerability, and the score says nothing about your estate. Is the affected version running? Can anyone beyond the host reach it? Checked by hand, host by host, the one exposed system waits in the same queue as the harmless ones.
The Certalert specialty takes each alert from your ticketing system. It finds where the affected software runs, in a Kubernetes pod, a container, a system service or a plain process, and whether the running version is really vulnerable. It establishes who can reach it, from the whole internet down to the host alone, and what protects it, such as authentication. Each alert comes back with a reclassified severity, the reason, the evidence and a recommendation. Severity comes down only on solid evidence, and stays up when in doubt.

Which systems does it cover? RHEL-based Linux such as Rocky Linux, including software running in containers and Kubernetes on those systems.
What goes straight to a person? A vulnerable service open to the internet without authentication, signs of exploitation, an actively exploited vulnerability, or a case it cannot settle with confidence.
Each page is one kind of ticket, and how this specialty handles it within the limits you set.
> READY_TO_DEPLOY
Book a technical demo and walk through your own environment with the 2501 team.